Trust built into every decision
Customer boundaries, policy controls and accountable execution are fundamental design requirements.
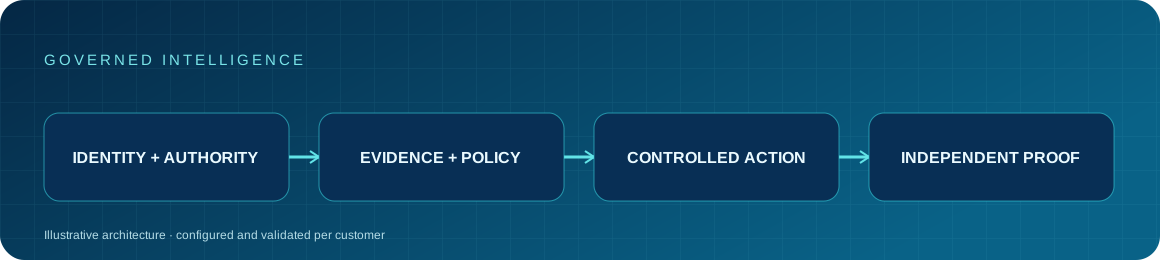
Privacy and protection
Security statements describe intended design controls, not independently certified deployment claims.
Tenant isolation
Isolated customer data and memory layers with enforced access boundaries.
Identity and least privilege
Role-based permissions, delegated authority and constrained integrations.
Evidence lineage
Source references, decision records and auditable action history.
Retention and legal holds
Governed lifecycles for retention, holds and authorized deletion.
Independent verification
Separate checks of action outcomes and recovery status.
Security validation
Testing, threat review and deployment-specific assurance are required before claims of compliance.
Security is a design requirement, not a slogan
Ceryvra’s intended architecture separates customer workspaces, constrains actions to authorized roles and delegated authority, and links decisions to evidence. Independent verification is designed to check actual state rather than relying on a tool’s success message. Retention, legal holds, audit history and revalidation obligations support responsible governance.
Controls and integrations must be tested in their deployed environment. Ceryvra does not claim certification, guaranteed outcomes or completed third-party audits without evidence.